Every time a high-profile breach hits the headlines, the predictable chorus begins. Headlines shriek about compromised government files, leaked blood panels, and exposed spouse details, painting a picture of an unprecedented digital catastrophe. Editorial boards clutch their pearls and demand immediate investigations, tougher firewalls, and stricter compliance mandates. Society loves a good breach narrative because it offers a clean villain: a faceless hacker breaking into a pristine fortress.
It is all a comforting, dangerous fairy tale.
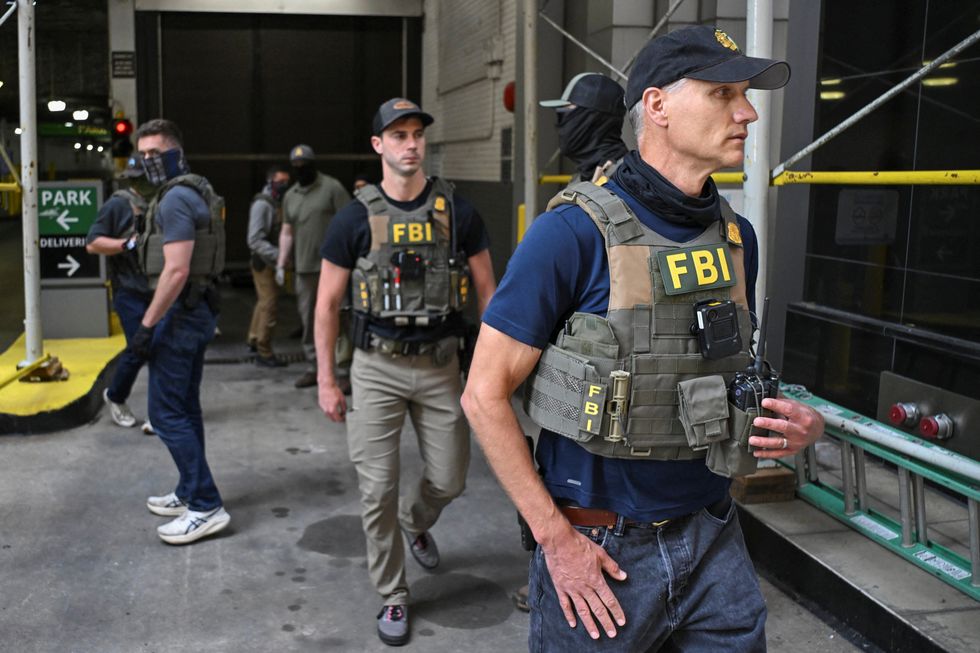
I have watched organizations spend millions on perimeter defense while leaving the back door wide open with legacy software and sloppy credential management. The outrage over the recent FBI file leaks misses the entire point of how modern information architecture works. The shock isn't that federal files containing medical records and family histories were accessed by unauthorized actors. The shock is that anyone still believes absolute digital privacy exists within a bureaucratic state apparatus that hoards dossiers on citizens by design.
To understand why the mainstream panic over this breach is misguided, you have to dismantle the lazy consensus surrounding digital security, institutional data collection, and the actual value of the information supposedly stolen.
The Bureaucratic Panopticon and the Myth of the Air-Gapped Life
The prevailing public narrative treats the government and large institutions as innocent victims of malicious outsiders. This framing is fundamentally dishonest. Federal agencies, healthcare providers, and corporate conglomerates do not collect personal information out of accidental convenience. They gather it because data accumulation is the currency of modern governance and commerce.
When reports surface that medical metrics, blood tests, and dependent details were exposed, the public reacts as if a sacred vault of personal intimacy has been violated. Let us be precise about what these files actually represent. A government background check or personnel file does not contain a diary or a soul. It contains standardized markers: cholesterol counts, blood pressure readings, vaccination records, emergency contacts, and marital relationships. These are bureaucratic checkpoints used to assess risk, clearance, and operational reliability.
The myth is that these files were ever secure in any meaningful sense. In any system complex enough to manage millions of personnel records across decentralized networks, vulnerability is a mathematical certainty. When you centralize vast pools of sensitive human data, you build a honeyed trap. Hackers do not need to invent new physics to breach these systems; they simply exploit the inherent human and structural rot that plagues every large-scale database.
Blaming the breach entirely on the intrusion ignores the architects who decided to collect, store, and indefinitely retain that information in the first place. If you do not want your medical data exposed in a cyberattack, the only foolproof method is refusing to let institutions archive it. Complaining about the leak while defending the continuous expansion of state and corporate data hoarding is peak cognitive dissonance.
The Hypocrisy of the Data Broker Economy
Let us examine the staggering hypocrisy of the public outcry. While citizens lose sleep over a government agency leaking medical indicators and family ties, multi-billion-dollar data broker networks legally buy, sell, and cross-reference infinitely more granular health data every single day without a single subpoena.
Legal data brokers scrape pharmacy purchase histories, fitness tracker telemetry, insurance claim logs, and location pings from mobile applications. They know your resting heart rate, your grocery store purchases, your sleeping patterns, and your familial associations long before a federal file ever notes them. This information is packaged into consumer profiles and sold to advertisers, insurance underwriters, and corporate employers with minimal regulatory friction.
Yet, when a state-sponsored hacker or an independent cybercriminal downloads a batch of federal personnel files, society acts as though an unbreachable sanctuary has fallen. This is institutional gaslighting. The outrage is not driven by a genuine love for privacy; it is driven by the ego-bruising realization that the government is just as sloppy with its data vaults as the corporate entities we feed every time we tap a screen.
The stolen medical data and spouse details feel invasive because they carry a government letterhead. Strip away the seal, and the contents are identical to the digital shadow every single adult willingly builds for themselves online through convenience apps, loyalty cards, and unsecured web browsing.
The Zero-Sum Game of Perimeter Defense
The standard prescription offered by cybersecurity pundits in the wake of such breaches is predictable: increase spending on security tools, adopt advanced encryption protocols, and hire more consultants. This advice is a multi-billion-dollar racket designed to keep security vendors rich while solving nothing.
Perimeter defense is a failing model. In a world of distributed networks, remote workforces, legacy integration, and social engineering, absolute containment is an impossibility. Every wall can be scaled; every key can be stolen or compromised via a compromised credential or a tired employee clicking a phishing link at four in the afternoon.
When we focus solely on stopping the breach, we ignore the structural vulnerability of the data itself. The most effective security strategy is data minimization. If an agency does not collect a specific piece of health data, hackers cannot steal it. If a personnel file does not require a deep archive of spouse details and medical checkups to determine basic employment eligibility, that liability is instantly erased.
Organizations refuse to practice data minimization because information is power, and bureaucracies never voluntarily surrender power. They prefer to treat data security as an eternal game of whack-a-mole, buying more software licenses and shifting blame downward when the inevitable breach occurs. The recent FBI file leaks are a natural consequence of this philosophy. Until leadership shifts from storing everything forever to destroying what is unnecessary, every fortress remains a paper house.
What the People Also Ask Queries Get Wrong
A quick look at common search queries surrounding this topic reveals a deep confusion about risk and remediation. People want to know: How can I protect my personal medical data from being leaked online? or What happens if my family details are exposed in a government hack?
The premise of these questions is flawed because it assumes individual control over institutional databases. You cannot protect your data once you hand it over to a third-party monolith. Asking how to keep your medical records safe inside a federal server is like asking how to keep your house dry while living underwater. The environment itself is the hazard.
For the individual whose records are exposed in a breach, the practical reality is rarely the Hollywood-style identity theft drama portrayed in media alerts. Your blood test results and spouse's name sitting on a server in an unknown forum do not instantly ruin your credit score or drain your bank account. In most cases, this data is noise. It joins the vast ocean of leaked credentials already circulating in underground markets.
The real danger is not targeted extortion based on your cholesterol levels; it is the broader realization that the machinery protecting your life has feet of clay. The anxiety should not be directed at the thief who picked the lock, but at the architects who left the windows wide open while claiming to run a vault.
Unconventional Action: Starving the Beast
If you want a real solution instead of security theater, stop playing the compliance game and start practicing aggressive data minimization in your own professional and personal sphere.
First, audit every single application, employer questionnaire, and digital platform demanding unnecessary personal details. If a form asks for medical history or family lineage that has zero bearing on the core function, push back or provide sanitized inputs where legally permissible. Stop feeding the monster.
Second, accept that your data is already compromised. The moment you handed your health metrics to a hospital portal, your financial history to a credit bureau, or your background check to an employer, your digital footprint was copied, cached, and distributed across multiple redundant servers. Embracing this reality frees you from the paralyzing anxiety of trying to lock doors that were never truly bolted.
Finally, stop demanding better firewalls from organizations that treat your privacy as an afterthought. Demand legal liability for data hoarding. Force lawmakers to enact strict retention limits that compel institutions to purge sensitive medical and family records the moment they are no longer legally required.
The next time a major database leaks, do not waste energy clutching your pearls over the stolen files. Look past the headlines, ignore the vendors selling snake oil solutions, and recognize the breach for what it is: the inevitable collapse of a system built on collecting information it has no right to hold. Stop worrying about the hackers at the gate. The house was empty to begin with.