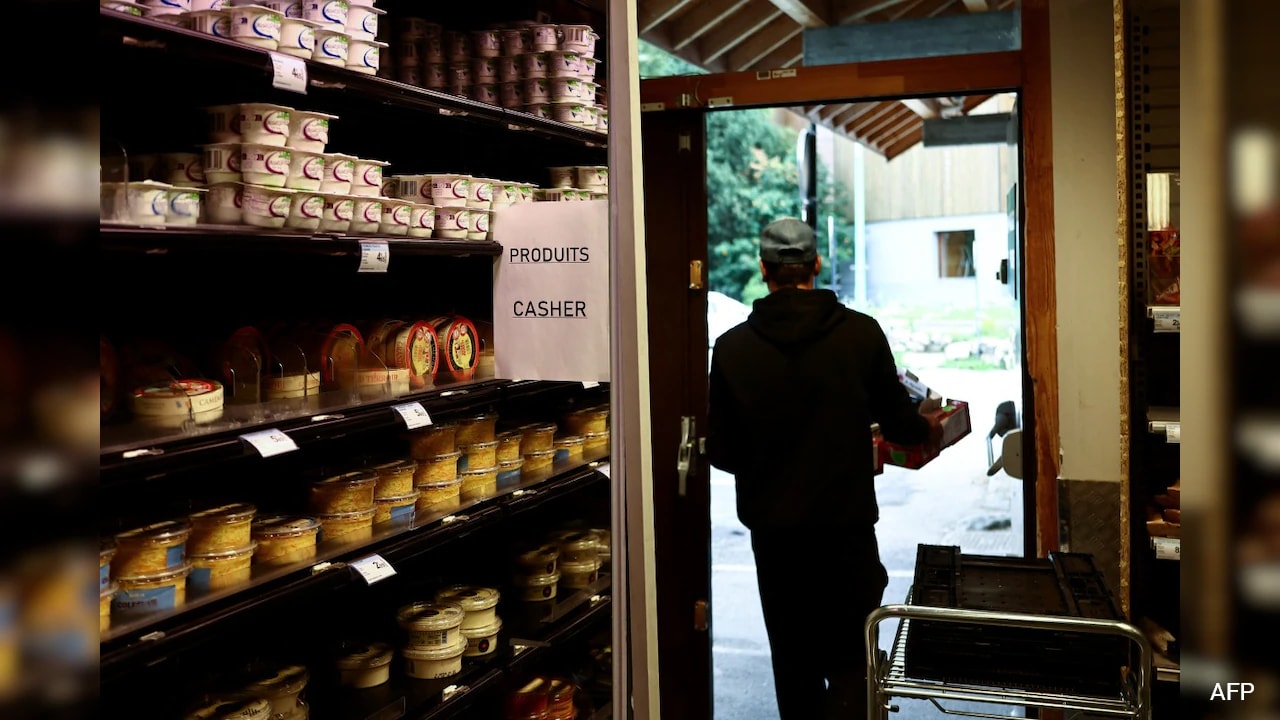
Modern supply chain infrastructure relies on tightly coupled digital management systems where a failure in software orchestration rapidly translates into physical disruption. When a cyberattack targets enterprise resource planning platforms or refrigeration telemetry units across national retail networks, the resulting crisis exposes the fragility of centralized automated logistics. This analysis deconstructs the mechanics, operational impact, and systemic vulnerabilities revealed by the widespread disruption of French supermarket refrigeration units following a malicious digital intrusion.
The Architecture of Retail Refrigeration Vulnerabilities
Commercial supermarket refrigeration networks are rarely isolated mechanical loops. To optimize energy consumption and comply with strict food safety regulations regarding cold chain integrity, modern stores deploy centralized Building Management Systems and digital supervisory control and data acquisition architectures. These systems govern compressor racks, evaporator fans, and thermal expansion valves via industrial internet of things protocols.
When external threat actors compromise these interconnected control layers, the attack vector bypasses traditional perimeter defenses by exploiting weak administrative credentials or unpatched vulnerabilities in third-party vendor management software. The primary mechanism of failure is not a physical destruction of hardware, but a software-level manipulation or lockdown. Attackers frequently deploy ransomware or logic-bomb scripts that disrupt supervisory controllers, severing the communication path between automated sensors and central cooling management consoles.
The Cascading Cost Function of Cold Chain Disruption
The economic impact of a prolonged refrigeration shutdown follows a non-linear trajectory. The cost function $C$ is determined by several compounding variables:
$$C = f(T, V, D, R)$$
Where $T$ represents the duration of thermal elevation above safety thresholds, $V$ denotes the total volume of perishable inventory compromised, $D$ accounts for the direct disposal and regulatory compliance costs, and $R$ measures brand erosion and consumer churn.
- Inventory Spoilage Thresholds: Perishable goods such as dairy, meat, and fresh produce have tightly bound time-temperature tolerance windows. Once refrigeration units lose power or automated control for more than a few hours, entire walk-in coolers and display cases must be written off to prevent public health violations.
- Logistical Paralysis: Restoring power manually requires physical inspection of every individual circuit breaker and refrigeration controller across hundreds of localized branches. Automated remote restarts are often locked out by malicious encryption keys or corrupted firmware, necessitating on-site engineering interventions.
- Regulatory Compliance and Liability: European food safety standards mandate strict traceability and temperature logging. A systemic cold chain failure triggers mandatory audits by sanitary agencies, resulting in potential fines and temporary store closures that compound lost revenue.
Operational Failures in Incident Response
Organizations targeted by sophisticated cyber-physical intrusions frequently suffer from delayed isolation protocols. The standard enterprise response to a ransomware event involves immediate network segmentation. However, in retail environments where point-of-sale terminals, inventory databases, and refrigeration telemetry share flat or poorly segmented local area networks, broad network quarantines inadvertently blind store managers to the operational status of physical assets.
The absence of analog fail-safes further exacerbates the crisis. When digital telemetry fails, legacy mechanical overrides are often poorly documented or require specialized technician access that is unavailable during off-hours. This creates a severe labor bottleneck, forcing retail operations to deploy scarce maintenance crews across geographically dispersed locations simultaneously.
Strategic Mitigation and Resilience Engineering
Defending large-scale retail infrastructure against coordinated cyber-physical attacks requires a fundamental shift from perimeter security to zero-trust network architecture within operational technology environments.
Enterprises must decouple refrigeration supervisory networks from corporate enterprise IT systems via air-gapping or unidirectional security gateways. Furthermore, mandatory implementation of hardware-level manual override switches enables store staff to maintain basic compressor operations even when central control servers are compromised. Risk management frameworks must transition from treating cybersecurity as an IT compliance checkbox to treating industrial control system integrity as an essential pillar of business continuity.